Blog post overview and metadata
Author, publish date, read time, and category
UK Cyber Security Checklist for Growing Businesses in 2026
Reviewed by: ARS Developer Team | Updated: 30 Sep 2026 | UK Focus: Buyer-intent SEO, web delivery, and measurable conversion growth.
Quick Summary
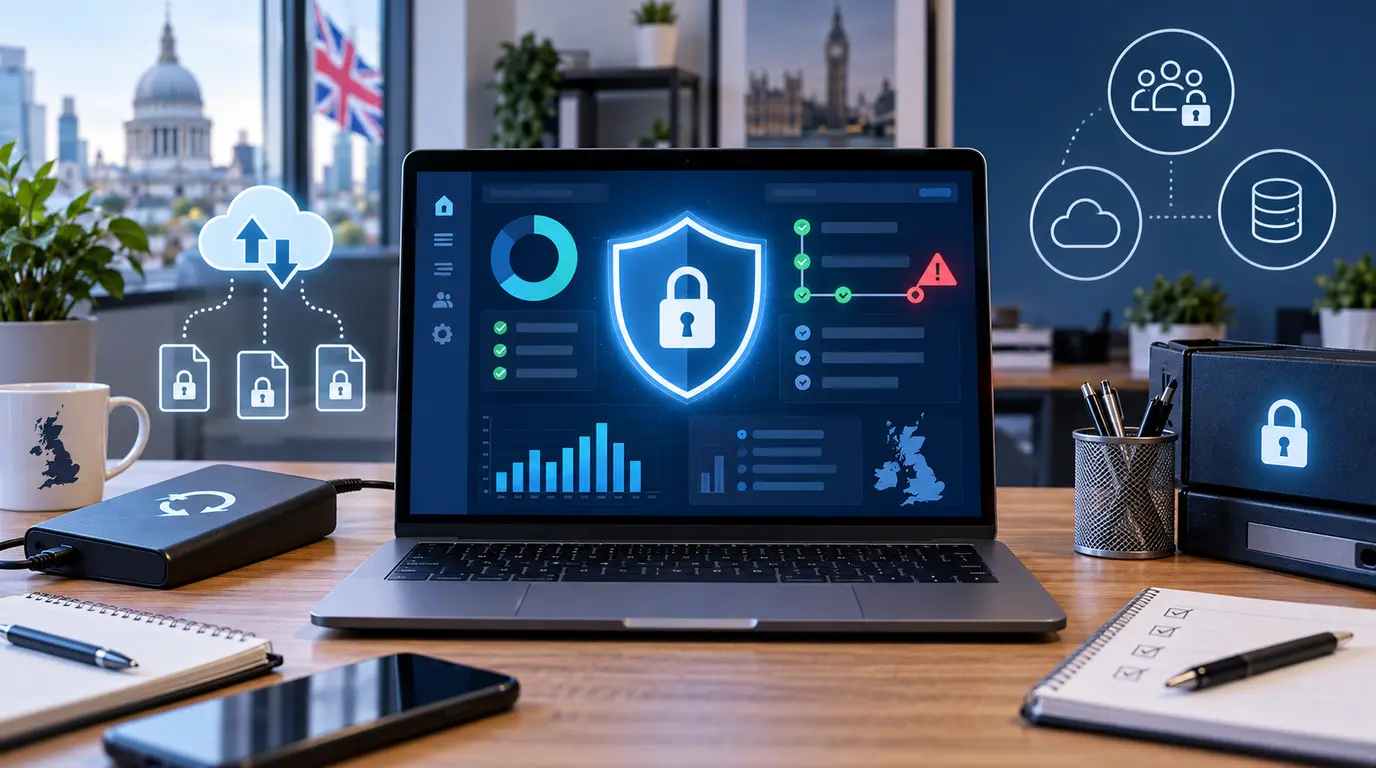
A UK-focused cyber security checklist for businesses that want stronger resilience, better governance, and safer growth in 2026.
In This Guide
Why This Article Is Trustworthy
- Reviewed by the ARS Developer editorial team for UK business relevance.
- Structured around buyer-intent SEO, technical delivery, and measurable conversion outcomes.
- Connected to related service pages, pricing guidance, and supporting articles for stronger topic depth.
Quick Answer
Cyber resilience is now an operating requirement for businesses whose website, email, CRM, and delivery systems all affect revenue.
Most risk comes from weak process control, unclear ownership, and poor recovery readiness rather than one dramatic technical flaw.
The first controls to review
- Assign clear cyber ownership.
- Audit MFA, admin accounts, and password hygiene.
- Review backup testing rather than backup claims.
- Protect website, hosting, email, and domain control.
- Train staff against phishing and impersonation attacks.
- Document incident response steps.
Why cyber resilience now affects growth
A breach or major outage can disrupt sales, delivery, invoicing, and reputation at the same time. That is why cyber cannot sit outside normal business operations anymore.
For software-heavy businesses, cyber planning overlaps with website management, CRM access, vendor control, and managed support quality.
Related planning areas
Read this with managed IT expectations, CRM process maturity, and technical website governance.
What buyers should verify before committing
Ask who owns hosting, email, MFA, backup testing, incident response, and domain access. Weak answers on these areas usually show a weak operational model behind the scenes.
For service-led businesses, stronger cyber hygiene also protects sales continuity, client trust, and delivery quality. That makes it a commercial decision as much as a technical one.
How cyber readiness protects operational growth
Cyber resilience is now closely tied to delivery continuity, lead handling, payment systems, and team productivity. In practical terms, weak cyber governance creates commercial drag even before a major incident happens.
That is why stronger controls often need to sit beside service delivery planning, system ownership, and supplier review rather than inside a purely technical checklist.
Questions leadership should ask right now
- Who owns domain, hosting, email, MFA, and backup testing?
- What happens operationally if a key account or system is compromised tomorrow?
- Which suppliers would the team contact first during a real incident?
Implementation checklist
- Document ownership of domains, hosting, backups, MFA, and supplier access before treating cyber readiness as complete.
Frequently Asked Questions
What is the most common cyber threat for UK businesses?
Phishing and credential compromise remain among the most common practical threats because they exploit process weakness, not just infrastructure weakness.
Is cyber security only an IT issue?
No. It is also a leadership, process, and governance issue because business-critical systems depend on clear ownership and response plans.
Further Reading
Continue with managed IT planning, service delivery scope, and our project planning process if resilience matters to your workflow.
Next Step
Our software systems, digital delivery services, and project planning support can be structured with resilience in mind from the start.
If resilience matters to your commercial workflow, the best next step is a practical review of ownership, recovery readiness, and supplier control. The strongest cyber improvements usually start with governance, not just tooling.
Next Step Resources
Move from research into action with the most relevant service, proof, pricing, and project planning pages for this topic.
Tags:

Leave a Comment
Ask a practical question, share a project insight, or add a useful note. Every comment is reviewed before it appears publicly.