Blog post overview and metadata
Author, publish date, read time, and category
UK SME Cyber Resilience 2026: Ransomware Backups, Access Control and Recovery Plans
Reviewed by: ARS Developer | Updated: 08 Sep 2026 | UK Focus: Buyer-intent SEO, web delivery, and measurable conversion growth.
Quick Summary
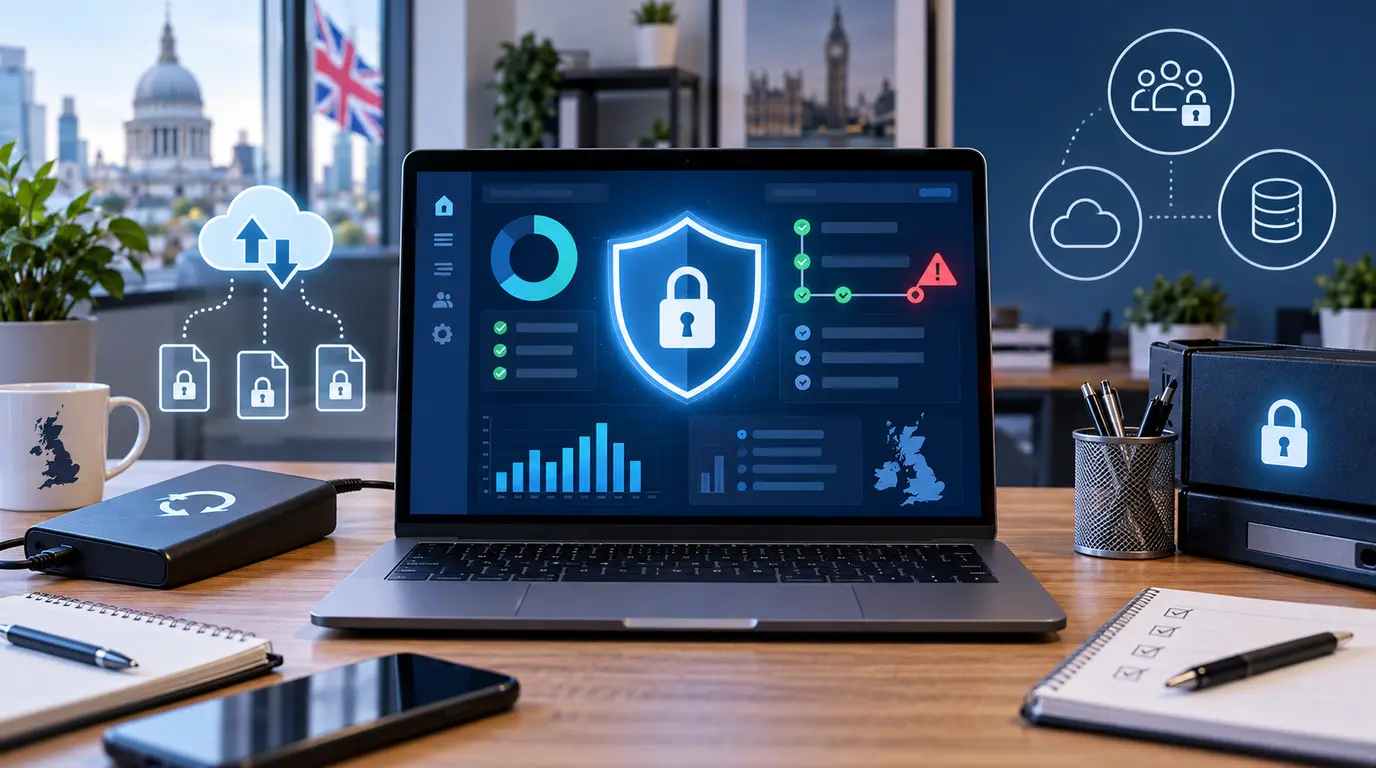
Cyber resilience for UK SMEs is about recovery as much as prevention. Build safer backups, stricter access, patch routines and a simple ransomware response plan before a bad week becomes a business crisis.
In This Guide
Why This Article Is Trustworthy
- Reviewed by the ARS Developer editorial team for UK business relevance.
- Structured around buyer-intent SEO, technical delivery, and measurable conversion outcomes.
- Connected to related service pages, pricing guidance, and supporting articles for stronger topic depth.
Cyber resilience for UK SMEs in 2026 is not about buying one security product and hoping for peace. It is about knowing how quickly you can recover when email is compromised, a laptop is stolen, ransomware appears, or a supplier account is abused. Prevention matters. Recovery decides whether the business survives the week.
The National Cyber Security Centre continues to publish practical guidance for small and medium-sized organisations because the basics still stop a large share of real-world damage. For smaller firms, the challenge is making those basics happen without a full IT department. This guide turns the essentials into an owner-friendly operating plan.
Start with the systems that make money
List the systems you could not trade without for three working days: email, website, CRM, accounting, files, payment platforms, booking tools, phones and admin laptops. Then write down who can access each one, whether two-factor authentication is enabled, how data is backed up and how you would restore it. That simple map usually reveals the real risk within an hour.
Do not start with abstract threats. Start with business interruption. If your CRM disappeared tonight, how many open leads would be lost? If email was locked, how would clients reach you? If the website was defaced, who could restore it? Cyber planning becomes easier when each answer is tied to revenue and trust.
Backups need restore tests
A backup you have never restored is a comforting theory. Ransomware planning requires three questions: is there an offline or immutable copy, how often is it made, and how long does restoration take? Cloud storage alone is not always enough, because synced files can sync the damage too.
A practical SME pattern is daily cloud backups for active systems, weekly offline or isolated backups for critical data, and a monthly restore test. The restore test does not need theatre. Pick one file set, one database or one website snapshot and prove it can come back. Record the time taken and the person responsible.
Access control is the cheapest upgrade
Many incidents become serious because too many people have too much access. Former staff keep logins. Contractors share admin accounts. A junior user can export all customer data. A password reused on a supplier portal opens the main mailbox.
Fix access with a quarterly review. Remove dormant users, enforce two-factor authentication, use named accounts, limit admin rights and keep a password manager. For systems containing client records or financial data, make access a business decision, not an informal favour.
Patch routines without drama
Software updates are not glamorous, but unpatched websites, plugins and laptops are a common route into small businesses. Set a monthly patch window for devices and a separate website maintenance routine. If your website is WordPress, plugin hygiene is essential. If it is Laravel or another custom stack, framework and package updates still need ownership.
ARS Developer handles this through structured maintenance for client systems: backups, updates, uptime checks, error monitoring and measured releases. You can explore our web development and custom software services if your current setup has no clear maintenance owner.
The ransomware call sheet
When an incident happens, people make poor decisions under pressure. Write a one-page call sheet now. Include the owner, IT supplier, web developer, accountant if finance systems are involved, insurer, bank fraud line, hosting provider and any legal or data protection support. Add account recovery links and emergency phone numbers. Store a printed copy away from the affected systems.
The first hour should be calm and mechanical: disconnect affected devices, preserve evidence, stop password reuse from spreading, contact the right support, check backups, and communicate only what you know. Avoid rushing to pay attackers or wiping evidence before advice is taken.
Client trust after an incident
Technical recovery is only half the job. Clients need clear communication: what happened, what data may be affected, what you are doing, and what action they should take. Vague reassurance damages confidence. Honest, specific updates restore it faster.
This is another reason to keep clean system records. If you know which clients were in which system, what was backed up, and who had access, your response becomes factual instead of panicked.
Official guidance worth using
The NCSC's small and medium-sized organisation guidance is written for this exact audience. Treat it as a baseline, then adapt the steps to your own systems, suppliers and recovery needs.
A simple maturity ladder
Level one: two-factor authentication, password manager, named users and daily backups. Level two: monthly patching, quarterly access reviews, restore testing and staff phishing awareness. Level three: incident call sheet, supplier risk review, logging, endpoint protection and Cyber Essentials alignment. Most UK SMEs can reach level two quickly and should treat level three as a sensible 2026 target.
How ARS Developer can help
We can review your website, hosting, CRM and internal software for the recovery gaps that cause the most pain. Then we can implement monitoring, backups, access controls and maintenance routines that fit a small business budget. Send us your setup and we will tell you where the weak points are before they become expensive.
Next Step Resources
Move from research into action with the most relevant service, proof, pricing, and project planning pages for this topic.
Tags:























Leave a Comment
Ask a practical question, share a project insight, or add a useful note. Every comment is reviewed before it appears publicly.